09 / Self-service experiences
Member workspace
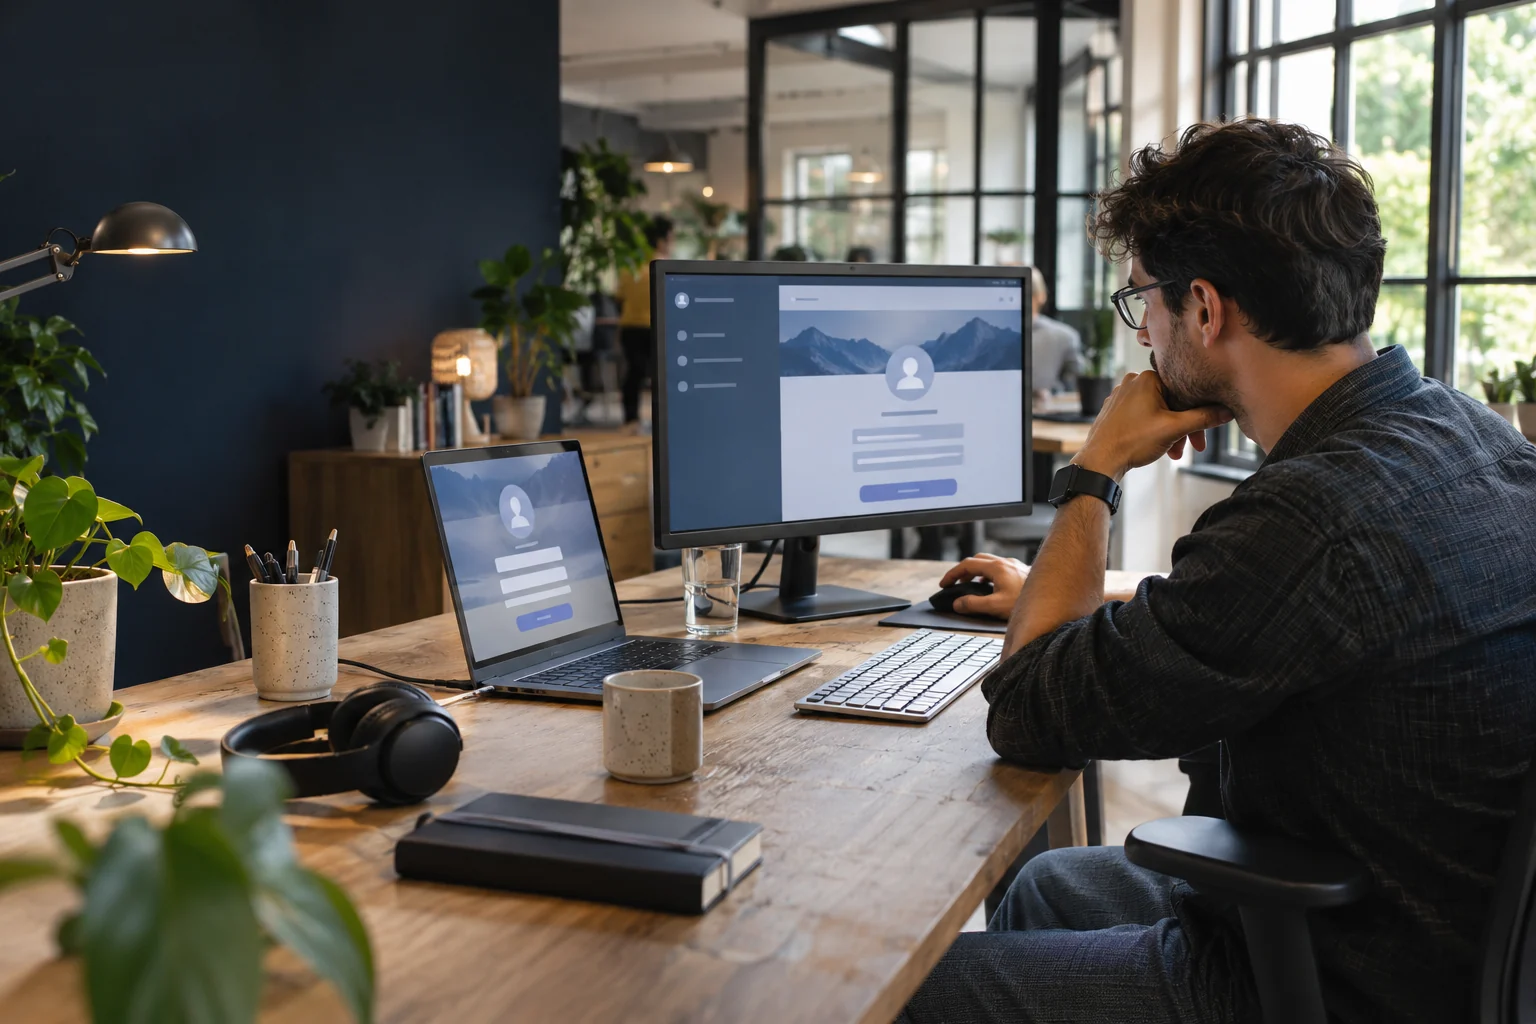
A private space for sharing resources, updating simple information and giving each profile a suitable starting point.
THE PROBLEM TO MAKE SIMPLER
Access that fits the person using it.
A shared folder is often a compromise between too much visibility and too many access requests. A dedicated space makes public, restricted and administrative content distinct.
FOCUS / 09
We start with up to three roles and a small resource set. Identity, permissions and leaving the service are scoped before screens are developed.
TRY THE IDEA
Interactive illustration with fictional data. Not a live product or a client result.
THE FIRST SCOPE
What we scope.
- 01An agreed sign-in mechanism
- 02Three roles and explicit permissions
- 03A resource library and a simple profile record
- 04Access management and administration notes
AT THE END OF THE SCOPESomething to use.
Something to use.
And enough to take it over.
Permissions matrix and associated tests
Administration and access-closure guide
BEFORE STARTINGTwo questions
Two questions
that matter.
Can members see one another’s information?
Only where a legitimate, disclosed need is agreed. Permissions are limited by default; profiles are not a public directory.
Is security guaranteed forever?
No. Permissions, updates and providers need ongoing attention. Operation and maintenance are agreed separately.
↳
In the same domain.
Self-service experiences
Learning pathway
Useful content deserves a readable route.
From €2,400Explore ↗
THE RIGHT NEXT STEPStart with a situation.
Start with a situation.
Not a ready-made answer.
Tell us what slows down your day. Together we can define the first useful scope.
Prepare my enquiry